2026/ 2027 CMMC RESEARCH REPORT
Committed to the Mission: The State of the DIB with CMMC in Flux
What’s really happening across the DIB as CMMC evolves?
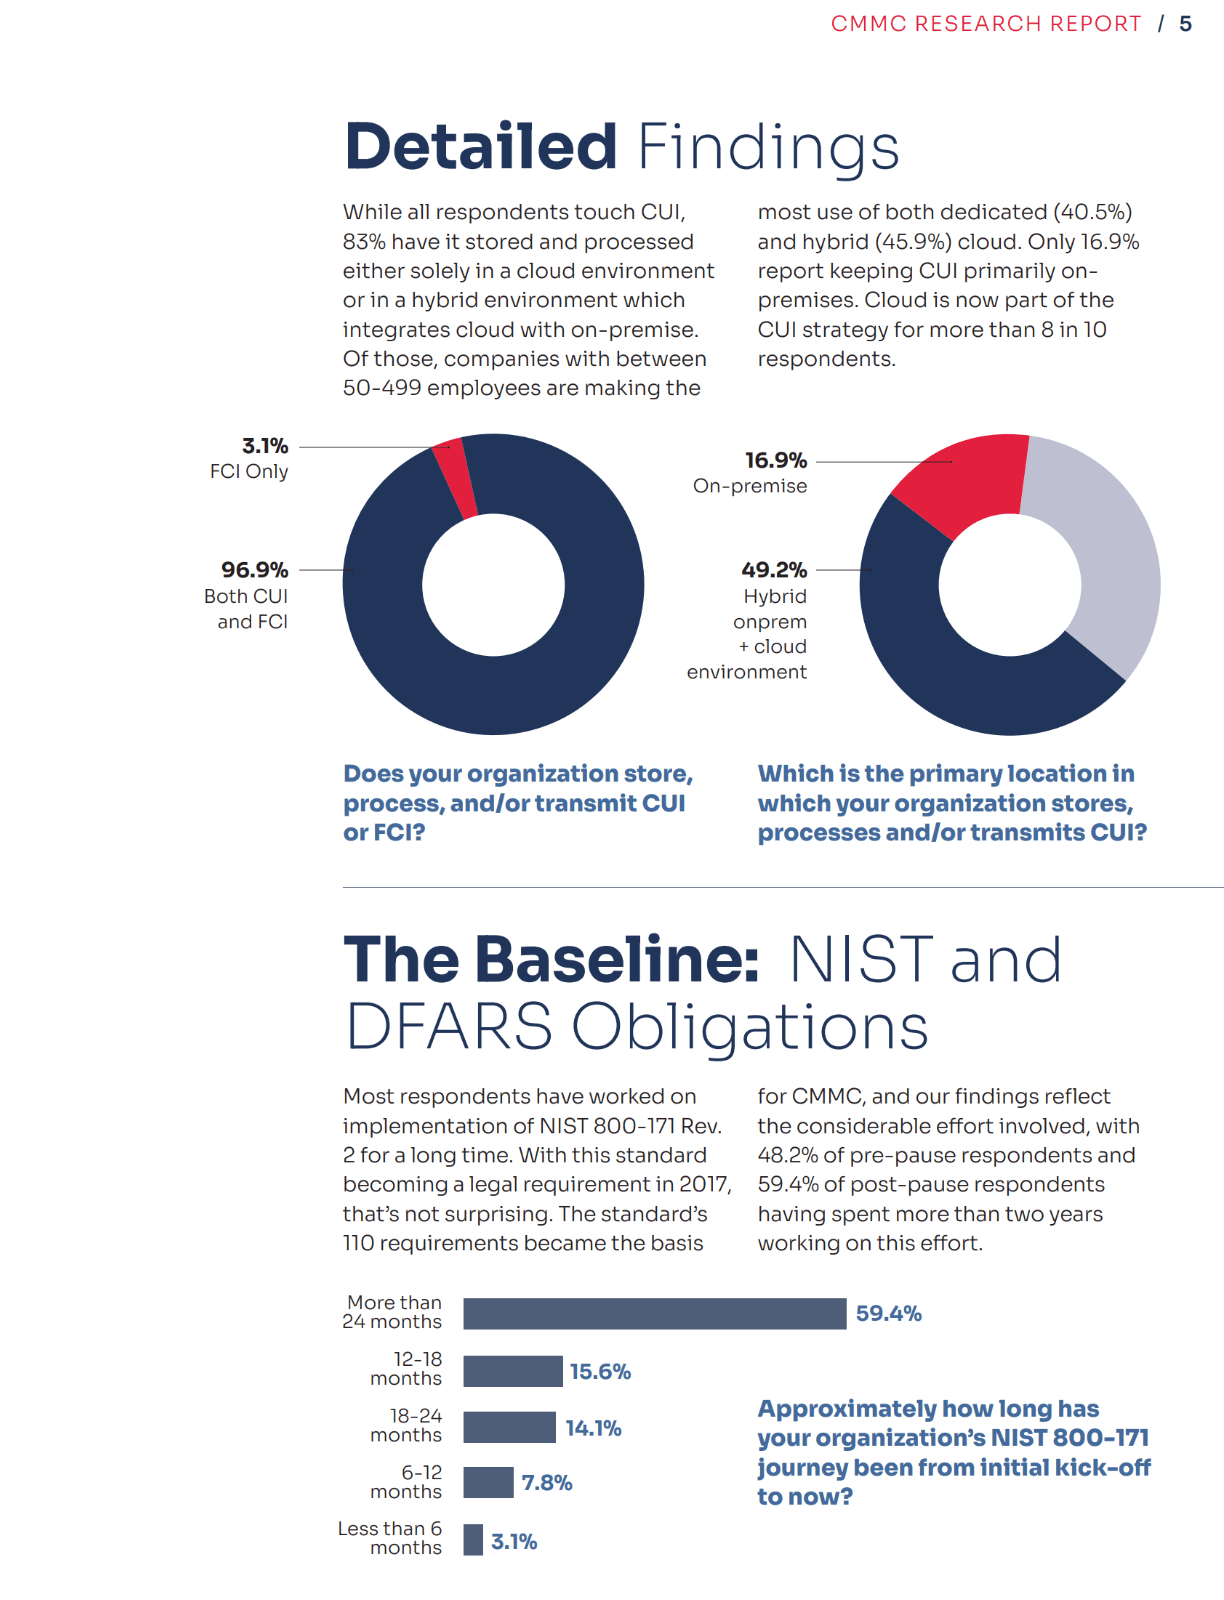
For the third year, Redspin surveyed the Defense Industrial Base to understand how contractors are navigating CMMC and the cybersecurity requirements behind it. This year’s report gives you a look at how your peers are responding to the pause, where they’re investing, and what they’re prioritizing.
What the DIB Told Us
Nearly 8 in 10
Are staying the course toward certification or have already achieved Level 2.
75%
Still believe Level 2 certification provides value.
68.8%
Cite independent cybersecurity validation as part of that value.
The mission hasn’t paused. Neither should the work to protect it.
CMMC requirements may continue to evolve. The threats to sensitive defense information will too.
Our research points to a DIB that has already invested years in stronger environments, technologies, processes, and people. The question now isn’t simply what happens to CMMC. It’s whether cybersecurity investment keeps pace with the threat.
The report explores what these findings mean for cybersecurity investment, CMMC readiness, prime and subcontractor expectations, and the decisions contractors are making about what comes next.
Voices From the DIB
What stood out to me is that even among organizations that have slowed their CMMC efforts, many haven’t stopped working on the underlying cybersecurity requirements. That’s encouraging. CMMC may be in flux, but DFARS and NIST obligations haven’t gone away, and neither has the responsibility to protect CUI.
Robert Teague, VP, and Lead CCA, Redspin
While there may be uncertainty around CMMC timelines and how the program continues to evolve, our responsibility to protect CUI and sensitive defense information has not changed. We are continuing to move forward toward CMMC Level 2 because protecting the information entrusted to us is ultimately the objective, regardless of the certification timeline.
– Ashley R. Pedersen,Director of Information Technology, Maritime Tactical Systems, Inc.
Cybersecurity cannot be separated from quality, reliability, or performance. That’s why we see the work behind CMMC L2 C3PAO assessments as more than a compliance requirement, it strengthens the trust and security that have to be built into everything we deliver.
– JohnE Mullin,Director, Information Technologies, Trenton Systems
A Donation With a Mission
For every completed survey, Redspin pledged $10 to the Gary Sinise Foundation, an organization dedicated to supporting our nation’s defenders, veterans, first responders, and their families. Thanks to survey participants, we’re proud to donate $1,310 to support programs that honor and strengthen those who serve.
Subscribe to the Redspin Newsletter
CMMC updates, compliance guidance, and federal agency cybersecurity insights delivered to your inbox.