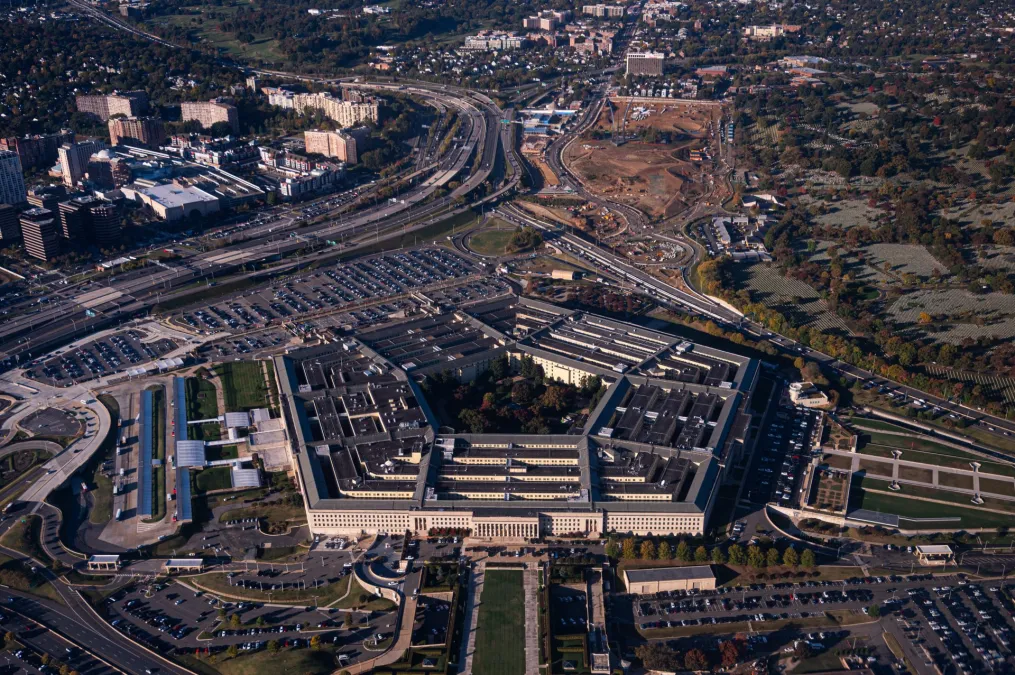
What the Pentagon’s new post-quantum cryptography directive means for defense contractors
The Defense Department wants to introduce PQC requirements into the CMMC program, but experts warn industry and the underlying technology is far from ready.
The Defense Department wants to introduce PQC requirements into the CMMC program, but experts warn industry and the underlying technology is far from ready.
Redspin’s Thomas Graham breaks down why CMMC costs are catching many DoD contractors off guard, explaining that the real financial burden stems from years of delayed cybersecurity compliance, not the certification itself.
Thomas Graham discusses assessment demand, costs, readiness timelines, and the rigor of CMMC assessments.
The entire DIB must remember that CMMC compliance is a continual journey that is necessary to protect our warfighters and our nation.
Independent Third‑Party Validation Reinforces Redspin as a Trusted External Service Provider (ESP) for the Defense Industrial Base
Organizations instinctively assign complete cybersecurity ownership to information technology (IT). Multifactor authentication, phishing drills, security awareness training and virtual private networks are all visible markers of a “serious” program, and they all live within the IT function.